A supplier’s bank details change
This scenario was published by the Australian Signals Directorate’s Australian Cyber Security Centre in its Small business cyber security guide (January 2025).
A small construction business received an email from their supplier saying they had changed banks. The supplier provided new account details for invoice payments. Because the email seemed legitimate, the construction business did not call the supplier to confirm the change in bank account details.
The business paid an invoice from the supplier for over $70,000. The following day, another employee mistakenly paid the same invoice again for an additional amount over $70,000. In total, over $150,000 was paid to the new bank account.
When the business rang their supplier to ask if they could refund the duplicate payment, the supplier advised those banking details were incorrect. An investigation was launched immediately, and the supplier discovered that one of their email accounts had been hacked and was sending out fraudulent bank account details. No funds were recovered.
Australian Signals Directorate’s Australian Cyber Security Centre (2025), Small business cyber security guide, January, p. 5, “Email attacks”, case study. © Commonwealth of Australia. Reproduced under CC BY 4.0; wording unchanged, paragraph layout adapted. The analysis below is by Plain Risk.
Describe the risk before payment
The construction business could lose the invoice payment by transferring it to a fraudulent account after receiving changed bank details. The Describe a risk tool provides a simple representation of the risk.
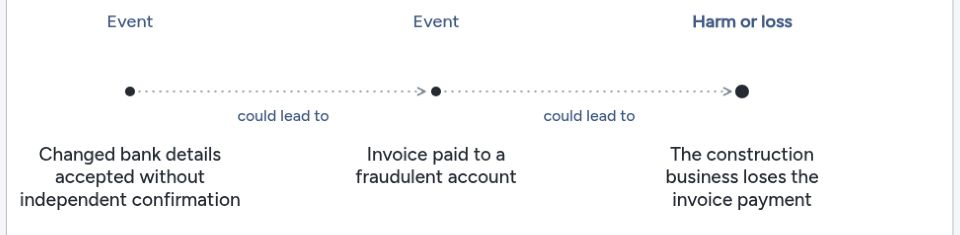
The diagram does not include the duplicate payment which increased the loss through a separate error.
Propose a control
As a control, the ACSC advises calling to confirm changed bank details using contact details obtained independently of the request.
The Assess a control tool provides a clear representation of how this proposed control would work.
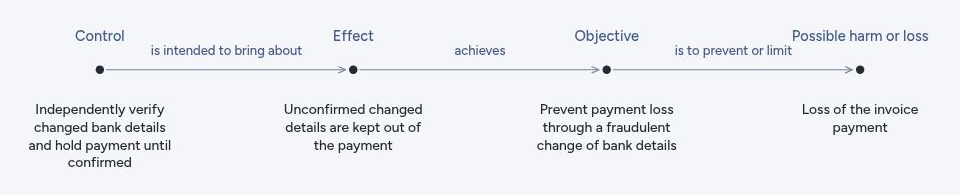
Once the control is mapped, the Design and Effectiveness tabs help users test and assess the control.
Plain Risk, developed by Dr Julien Maréchal. © 2026 The Governance Practice.
Original materials:  CC BY 4.0. Source. Scope and attribution.
Logos, third-party material, and website software are excluded.